Sunday, May 7, 2023

Dragon Breath APT Group Using Double-Clean-App Technique to Target Gambling Industry

An advanced persistent threat (APT) actor known as Dragon Breath has been observed adding new layers of complexity to its attacks by adopting a novel DLL side-loading mechanism. "The attack is based on a classic side-loading attack, consisting of a clean application, a malicious loader, and an encrypted payload, with various modifications made to these components over time," Sophos researcher
http://dlvr.it/SnfSsm

Saturday, May 6, 2023

Fleckpe Android Malware Sneaks onto Google Play Store with Over 620,000 Downloads

A new Android subscription malware named Fleckpe has been unearthed on the Google Play Store, amassing more than 620,000 downloads in total since 2022. Kaspersky, which identified 11 apps on the official app storefront, said the malware masqueraded as legitimate photo editing apps, camera, and smartphone wallpaper packs. The apps have since been taken down. The operation primarily targets users
http://dlvr.it/SncS2m
Thursday, May 4, 2023

Hackers Exploiting 5-year-old Unpatched Vulnerability in TBK DVR Devices

Threat actors are actively exploiting an unpatched five-year-old flaw impacting TBK digital video recording (DVR) devices, according to an advisory issued by Fortinet FortiGuard Labs. The vulnerability in question is CVE-2018-9995 (CVSS score: 9.8), a critical authentication bypass issue that could be exploited by remote actors to gain elevated permissions. "The 5-year-old vulnerability (
http://dlvr.it/SnVsWw

Wednesday, May 3, 2023

North Korea's ScarCruft Deploys RokRAT Malware via LNK File Infection Chains

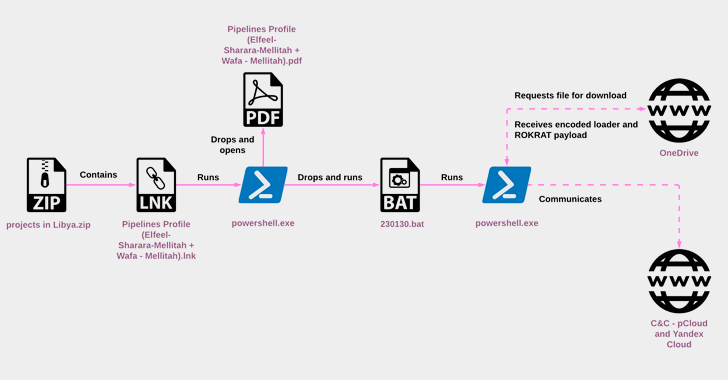
The North Korean threat actor known as ScarCruft started experimenting with oversized LNK files as a delivery route for RokRAT malware as early as July 2022, the same month Microsoft began blocking macros across Office documents by default. "RokRAT has not changed significantly over the years, but its deployment methods have evolved, now utilizing archives containing LNK files that initiate
http://dlvr.it/SnRvWK

Monday, May 1, 2023

Google Blocks 1.43 Million Malicious Apps, Bans 73,000 Bad Accounts in 2022

Google disclosed that its improved security features and app review processes helped it block 1.43 million bad apps from being published to the Play Store in 2022. In addition, the company said it banned 173,000 bad accounts and fended off over $2 billion in fraudulent and abusive transactions through developer-facing features like Voided Purchases API, Obfuscated Account ID, and Play Integrity
http://dlvr.it/SnLKTT

Cybersecurity needs AI as much as AI needs cybersecurity - Techzine Europe

Cybersecurity needs AI as much as AI needs cybersecurity  Techzine Europe http://dlvr.it/TDY1dr