Friday, May 12, 2023

Andoryu Botnet Exploits Critical Ruckus Wireless Flaw for Widespread Attack

A nascent botnet called Andoryu has been found to exploit a now-patched critical security flaw in the Ruckus Wireless Admin panel to break into vulnerable devices. The flaw, tracked as CVE-2023-25717 (CVSS score: 9.8), stems from improper handling of HTTP requests, leading to unauthenticated remote code execution and a complete compromise of wireless Access Point (AP) equipment. Andoryu was 
http://dlvr.it/SnwFBQ

Thursday, May 11, 2023

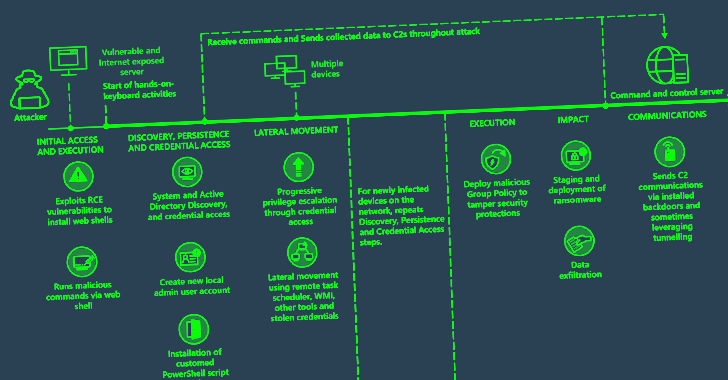
U.S. Government Neutralizes Russia's Most Sophisticated Snake Cyber Espionage Tool

The U.S. government on Tuesday announced the court-authorized disruption of a global network compromised by an advanced malware strain known as Snake wielded by Russia's Federal Security Service (FSB). Snake, dubbed the "most sophisticated cyber espionage tool," is the handiwork of a Russian state-sponsored group called Turla (aka Iron Hunter, Secret Blizzard, SUMMIT, Uroburos, Venomous Bear,
http://dlvr.it/SnsKlC
Wednesday, May 10, 2023

Microsoft Warns of State-Sponsored Attacks Exploiting Critical PaperCut Vulnerability

Iranian nation-state groups have now joined financially motivated actors in actively exploiting a critical flaw in PaperCut print management software, Microsoft disclosed over the weekend. The tech giant's threat intelligence team said it observed both Mango Sandstorm (Mercury) and Mint Sandstorm (Phosphorus) weaponizing CVE-2023-27350 in their operations to achieve initial access. "This
http://dlvr.it/SnpPxV

Tuesday, May 9, 2023

How to Set Up a Threat Hunting and Threat Intelligence Program

Threat hunting is an essential component of your cybersecurity strategy. Whether you're getting started or in an advanced state, this article will help you ramp up your threat intelligence program. What is Threat Hunting? The cybersecurity industry is shifting from a reactive to a proactive approach. Instead of waiting for cybersecurity alerts and then addressing them, security organizations are
http://dlvr.it/SnlQPl

Monday, May 8, 2023

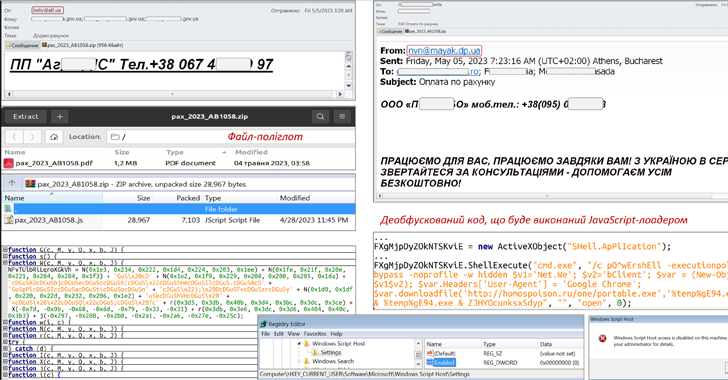
CERT-UA Warns of SmokeLoader and RoarBAT Malware Attacks Against Ukraine

An ongoing phishing campaign with invoice-themed lures is being used to distribute the SmokeLoader malware in the form of a polyglot file, according to the Computer Emergency Response Team of Ukraine (CERT-UA). The emails, per the agency, are sent using compromised accounts and come with a ZIP archive that, in reality, is a polyglot file containing a decoy document and a JavaScript file. The
http://dlvr.it/SnhYlK

Cybersecurity needs AI as much as AI needs cybersecurity - Techzine Europe

Cybersecurity needs AI as much as AI needs cybersecurity  Techzine Europe http://dlvr.it/TDY1dr